Get Your Pentest Report,In 5–7 Days.
Traditional pentest vendors take weeks to quote and months to deliver. Our rapid pentest allows you to start fast and get actionable security insights within days, not months, and ship a full security report — fast.




Speed Without Shortcuts
Automated scans are a great start — but real attackers don't stop there. Our professional pentesting uncovers vulnerabilities that tools can't.
AI-Prioritised Testing
Machine learning identifies the most likely attack vectors first, so our testers spend time on real threats, not false positives.
Expert Manual Verification
Every automated finding is validated by a human security expert. No generic scanner output — only real, exploitable issues.
Actionable Reports
Each finding includes risk ratings, proof of concept, and step-by-step remediation guidance your dev team can act on immediately.
ISO 27001 Ready
Reports are structured to satisfy ISO 27001 audit requirements. No extra formatting or rework needed for compliance.
Free Remediation Test
After you fix the issues we found, we retest to confirm the vulnerabilities are properly resolved — included in the price
Direct Expert Access
No ticket queues. You get direct access to the tester who worked on your engagement for questions and clarification.
How Rapid Pentest Works
Purchase
Choose your plan and buy your pentest instantly.
Scoping Call
A quick call to confirm targets, credentials, and any testing constraints.
Testing
AI-assisted automated scanning combined with expert manual exploitation testing.
Report
Detailed findings delivered within 5–7 days. A remediation test is included at no additional cost.
Sample Rapid Pentest Report
Every engagement delivers a detailed, professionally structured security report. Here's what to expect.
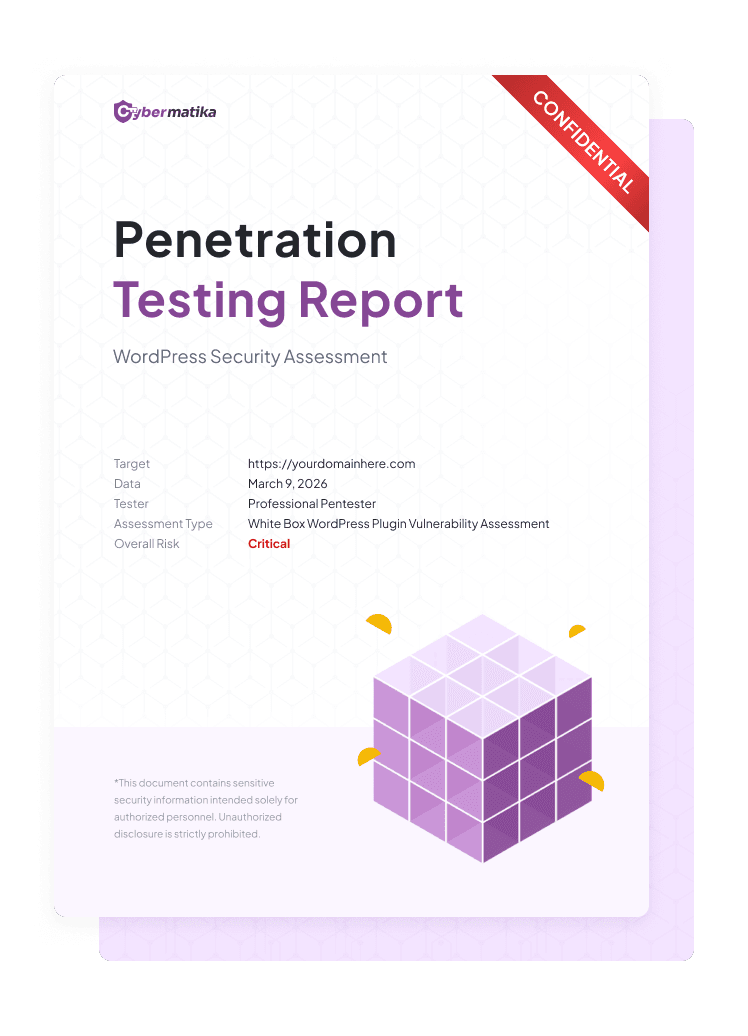
What's Inside the Report
Our Rapid Pentest report gives your team everything needed to understand your security posture and fix vulnerabilities fast.
- ✓Executive summary with overall risk rating
- ✓OWASP Top 10 — 2025 coverage assessment
- ✓Detailed findings with severity levels
- ✓Proof of concept for each vulnerability
- ✓Step-by-step remediation guidance
- ✓OWASP reference mapping per finding
Choose Your Security Service
Automated scans are a great start — but real attackers don't stop there. Our professional pentesting services uncover vulnerabilities that tools can't.
"Observatory++". Fully automated, AI-assisted, zero human touch.
FREE
- TLS/HTTPS Audit✓
- CVE/Component Scan✓
- DNS & Email SecurityPresences
- Security Headers CheckBasic
- Subdomain EnumerationLight
- API Testing✗
- Business Logic Testing✗
- API Regulated Industries✗
Limited by time, not scope. Manual + AI augmentation.
AUD 2,500 Fixed quote
- TLS/HTTPS Audit✓
- CVE/Component Scan✓
- DNS & Email Security+Misconfig
- Security Headers CheckExtended
- Subdomain EnumerationMedium
- API TestingLight
- Business Logic TestingCritical
- API Regulated Industries✗
Traditional pentest. Scoping, quoting, pentest, remediation.
CustomScope-based
- TLS/HTTPS Audit✓
- CVE/Component Scan✓
- DNS & Email SecurityDeep Audit
- Security Headers CheckFull Review
- Subdomain EnumerationFull
- API TestingFull
- Business Logic TestingFull
- API Regulated IndustriesFull
Pair It With Live Testing or a Deep Review
This scan covers your source code. If you also need live-environment testing or a full infrastructure review, these cover that ground.

AI Codebase Security Scan
A multi-agent AI review of your full codebase, cross-checked and signed off by a senior engineer, delivered as one prioritised report.

Technical Code Review
A deeper, two-week manual review of your codebase, tech stack, and infrastructure — with a prioritised risk register and roadmap.

AI & LLM Security Audit
Testing against the OWASP Top 10 for LLM Applications, for teams shipping chatbots, copilots, or agentic AI features.
Every Rapid Pentest Covers the OWASP Top 10
Broken Access Control
Users acting outside their intended permissions — privilege escalation, IDOR, forced browsing, and missing access checks.
Security Misconfiguration
Insecure default configs, open cloud storage, verbose error messages, missing security headers, and unnecessary services.
Software Supply Chain Failures
Vulnerable third-party components, unverified dependencies, and compromised build pipelines or update mechanisms.
Cryptographic Failures
Weak encryption, missing TLS, exposed secrets, insufficient key management, and plaintext data transmission.
Injection
SQL injection, XSS, command injection, LDAP injection — any untrusted input interpreted as code or queries.
Insecure Design
Missing or ineffective security controls at the design level — flawed business logic, missing rate limiting, and inadequate threat modelling.
Authentication Failures
Weak password policies, credential stuffing, brute force attacks, session fixation, and MFA bypass attempts.
Software & Data Integrity Failures
Unverified updates, insecure CI/CD pipelines, unsigned code, and data deserialization vulnerabilities.
Security Logging & Monitoring Failures
Insufficient logging, missing alerting, unmonitored access patterns that prevent breach detection and response.
Mishandling of Exceptional Conditions
Unhandled errors, crashes from unexpected input, and exception paths that leak data or create exploitable states.
Beyond the OWASP Top 10, our testers also assess these critical areas:
Common Questions
AI prioritises the most likely vulnerable areas and eliminates false positives from automated scanning. This means our security experts spend their time on real risks instead of chasing noise — cutting the overall engagement time significantly.
No. Automated scanning is only the first pass. Every finding is manually verified by an experienced penetration tester who also tests for business logic flaws and complex attack chains that scanners can't detect.
Yes. Our reports include documented findings, risk ratings, proof of concept, and remediation guidance — everything an auditor needs to see. Many of our clients use Rapid Pentest specifically for ISO 27001 compliance.
We work with you during the scoping call to define safe testing boundaries. Testing is designed to identify vulnerabilities without causing downtime or data loss to production systems.
Rapid Pentest covers the most common and critical attack surfaces. If you need a more comprehensive engagement — such as infrastructure testing, mobile apps, or red team exercises — talk to our security team about a Full Pentest.
Yes. The price you see is the price you pay. If scope changes are needed during the engagement, we discuss them with you before any additional work or cost is incurred.